

SC-200 sample exam questions
15 exam-style questions for Microsoft SC-200: Security Operations Analyst, with answers and explanations. Take them as a timed practice exam first if you want a score out of 1000.
- Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals. More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft 365 subscription.
You have 1,000 Windows devices that have a third-party antivirus product installed and Microsoft Defender Antivirus in passive mode.
You need to ensure that the devices are protected from malicious artifacts that were undetected by the third-party antivirus product.
Solution: You configure Controlled folder access.
Does this meet the goal?- AYes
- BNo
Show answer
Correct answer: B
WhyControlled folder access protects selected folders from unauthorized changes such as ransomware encryption, but it does not detect or remediate malicious artifacts the third-party antivirus missed, and it requires Defender Antivirus in active mode. EDR in block mode is the correct feature.
- A
- Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might
meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You have Linux virtual machines on Amazon Web Services (AWS).
You deploy Azure Defender and enable auto-provisioning.
You need to monitor the virtual machines by using Azure Defender.
Solution: You manually install the Log Analytics agent on the virtual machines.
Does this meet the goal?- AYes
- BNo
Show answer
Correct answer: B
WhyInstalling only the Log Analytics agent on AWS VMs does not make them Azure resources that Defender for Cloud can manage; they must be onboarded to Azure Arc first (directly or through the AWS connector). The Log Analytics agent is also retired, so this does not meet the goal.
- A
- You plan to create a custom Azure Sentinel query that will provide a visual representation of the security alerts generated by Azure Security Center.
You need to create a query that will be used to display a bar graph.
What should you include in the query?- Aextend
- Bbin
- Ccount
- Dworkspace
Show answer
Correct answer: C
WhyA bar chart needs aggregated values, so the query uses summarize count() by a column such as AlertName and then render barchart. bin is for time bucketing, extend adds calculated columns, and workspace() is for cross-workspace queries.
- A
- You have a custom Microsoft Sentinel workbook named Workbook1.
You need to add a grid to Workbook1. The solution must ensure that the grid contains a maximum of 100 rows.
What should you do?- AIn the grid query, include the take operator.
- BIn the grid query, include the project operator.
- CIn the query editor interface, configure Settings.
- DIn the query editor interface, select Advanced Editor.
Show answer
Correct answer: A
WhyAdding the take (limit) operator, for example take 100, to the grid's KQL query in the workbook restricts the result to at most 100 rows. project only selects columns, and the Settings and Advanced Editor options do not set a row limit.
- A
- DRAG DROP
You have an Azure subscription that contains two users named User1 and User2 and a Microsoft Sentinel workspace named workspace1.
You need to ensure that the users can perform the following tasks in workspace1:
• User1 must be able to dismiss incidents and assign incidents to users.
• User2 must be able to modify analytics rules.
The solution must use the principle of least privilege.
Which role should you assign to each user? To answer, drag the appropriate roles to the correct users. Each role may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
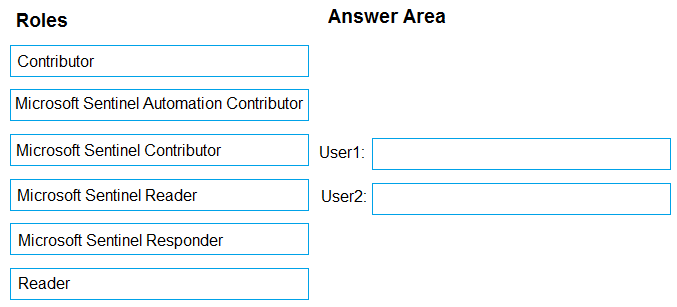
Move each item to the matching row:
- Contributor
- Microsoft Sentinel Automation Contributor
- Microsoft Sentinel Contributor
- Microsoft Sentinel Reader
- Microsoft Sentinel Responder
- Reader
- User1
- User2
Show answer
- User1 Microsoft Sentinel Responder
- User2 Microsoft Sentinel Contributor
WhyMicrosoft Sentinel Responder can manage incidents, including assigning and dismissing them, but cannot change analytics rules. Microsoft Sentinel Contributor is the least-privileged role that can create and edit analytics rules. Contributor would grant far more than needed.
- You have a Microsoft 365 E5 subscription.
You have a PowerShell script that queries the unified audit log.
You discover that the query returns only the first page of results due to server-side paging.
You need to ensure that you get all the results.
Which property should you query in the results?- A@odata.context
- B@odata.count
- C@odata.nextLink
- D@odata.deltaLink
Show answer
Correct answer: C
WhyMicrosoft Graph and audit log query APIs page results; each page includes an @odata.nextLink URL when more results exist. Your script must keep following nextLink until it is absent. @odata.count gives a total, @odata.context describes the schema, and @odata.deltaLink is for change tracking.
- A
- HOTSPOT
You have a Microsoft 365 E5 subscription.
You need to configure Microsoft Sentinel to collect logs from Microsoft Entra.
Which two nodes should you use in the Microsoft Defender portal? To answer, select the appropriate nodes in the answer area.
NOTE: Each correct answer is worth one point.
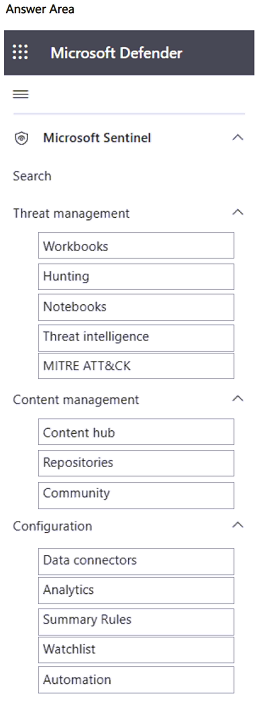
First node Workbooks / Hunting / Notebooks / Threat intelligence / MITRE ATT&CK / Content hub / Repositories / Community / Data connectors / Analytics / Summary Rules / Watchlist / Automation Second node Workbooks / Hunting / Notebooks / Threat intelligence / MITRE ATT&CK / Content hub / Repositories / Community / Data connectors / Analytics / Summary Rules / Watchlist / Automation Show answer
- First node Content hub
- Second node Data connectors
WhyData connectors ship in Content hub solutions. First install the Microsoft Entra ID solution from Content hub, then open Data connectors to configure the Microsoft Entra ID connector and choose the log types, such as sign-in and audit logs.
- You have an Azure subscription that has Microsoft Defender for Cloud enabled.
You have a virtual machine named Server1 that runs Windows Server 2022 and is hosted in Amazon Web Services (AWS).
You need to collect logs and resolve vulnerabilities for Server1 by using Defender for Cloud.
What should you install first on Server1?- Athe Microsoft Monitoring Agent
- Bthe Azure Monitor agent
- Cthe Azure Connected Machine agent
- Dthe Azure Pipelines agent
Show answer
Correct answer: C
WhyFor a Windows server in AWS, Defender for Cloud requires the server to be Azure Arc-enabled first by installing the Azure Connected Machine agent, directly or through the AWS connector. Log collection (Azure Monitor agent) and vulnerability assessment are then deployed as extensions. MMA is retired, and the Pipelines agent is for DevOps.
- A
- HOTSPOT
You have a Microsoft 365 E5 subscription that has a Conditional Access policy named Policy1.
You need to perform the following actions:
• Create a Conditional Access App Control custom policy named Custom1.
• Configure Policy1 to use Custom1.
What should you use co create Custom1, and in which settings of Policy1 should you enable Conditional Access App Control? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
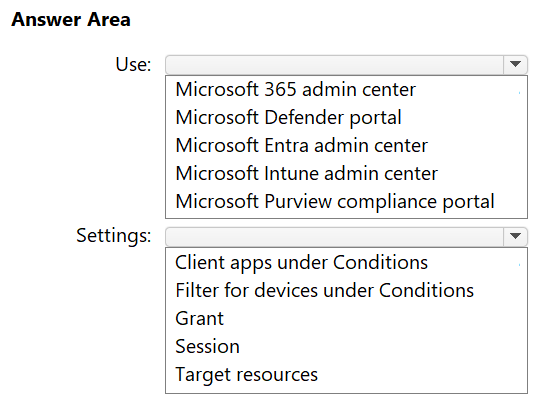
Use: Microsoft 365 admin center / Microsoft Defender portal / Microsoft Entra admin center / Microsoft Intune admin center / Microsoft Purview compliance portal Settings: Client apps under Conditions / Filter for devices under Conditions / Grant / Session / Target resources Show answer
- Use: Microsoft Defender portal
- Settings: Session
WhyCustom Conditional Access App Control (session or access) policies are created in Defender for Cloud Apps, which is now part of the Microsoft Defender portal. In the Entra Conditional Access policy, you enable Use Conditional Access App Control under Session and select Use custom policy.
- You have a Microsoft 365 subscription that uses Microsoft Defender XDR.
You are investigating an attacker that is known to use the Microsoft Graph API as an attack vector. The attacker performs the tactics shown the following table.
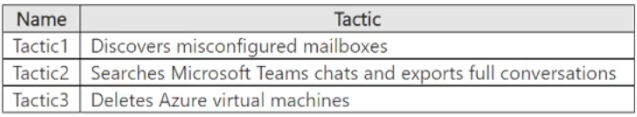
You need to search for malicious activities in your organization.
Which tactics can you analyze by using the MicrosoftGraphActivityLogs table?- ATactic1 only
- BTactic2 only
- CTactic1 and Tactic3 only
- DTactic2 and Tactic3 only
- ETactic1, Tactic2, and Tactic3
Show answer
Correct answer: E
WhyMicrosoftGraphActivityLogs records only requests to Microsoft Graph. Mailbox discovery and Teams chat export through Graph are logged, but deleting Azure VMs uses Azure Resource Manager, which appears in AzureActivity. No option lists exactly Tactic1 and Tactic2, so the intended answer treats all three as Graph-based.
- A
- HOTSPOT
You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint Plan 2 and contains a Windows device named Device1.
You initiate a live response session on Device1 and launch an executable file named File1.exe in the background.
You need to perform the following actions:
• Identify the command ID of File1.exe.
• Interact with File1.exe.
Which live response command should you run for each action? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
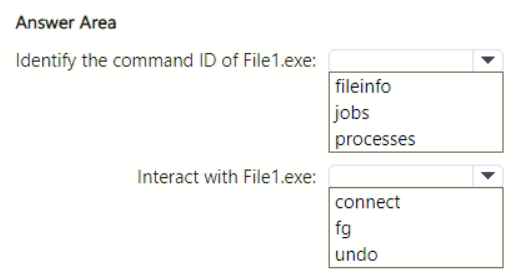
Identify the command ID of File1.exe: fileinfo / jobs / processes Interact with File1.exe: connect / fg / undo Show answer
- Identify the command ID of File1.exe: jobs
- Interact with File1.exe: fg
WhyThe jobs command lists commands running in the background with their command IDs. fg followed by the command ID brings that background job to the foreground so you can interact with it.
- HOTSPOT
You have a Microsoft Sentinel workbook that contains the following KQL query.
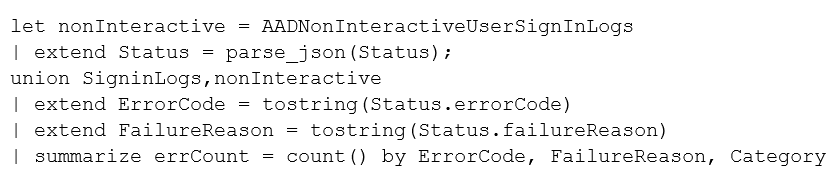
You need to create a visual that will change the color of the errCount column based on the value returned.
How should you configure the visual? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
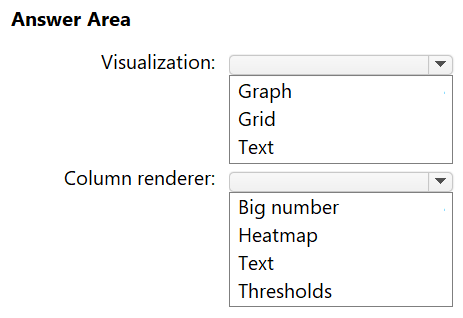
Visualization: Graph / Grid / Text Column renderer: Big number / Heatmap / Text / Thresholds Show answer
- Visualization: Grid
- Column renderer: Thresholds
WhyThe query returns tabular results, and only the Grid visualization offers per-column settings. Its Thresholds column renderer lets you set operators, values and colors, so the errCount cell color changes with the value returned. Text displays the value without any color rules.
- You have a Microsoft 365 subscription that uses Microsoft Defender for Endpoint Plan 2. The subscription contains 1,000 Windows 11 devices that run a third-party antivirus software and have Smart App Control enabled.
You need to ensure that if Defender for Endpoint detects a malicious artifact that was missed by the third-party software, it will remediate the artifact automatically.
What should you configure?- Aendpoint detection and response (EDR) in block mode
- BAllow or block file
- CAutomatically resolve alerts
- Dtamper protection
Show answer
Correct answer: A
WhyWith a third-party antivirus as primary and Defender Antivirus in passive mode, EDR in block mode lets Defender for Endpoint automatically block and remediate malicious artifacts detected by behavioral EDR sensors. Allow or block file is for indicators, automatically resolving alerts only closes alerts, and tamper protection protects settings.
- A
- You need to complete the query for failed sign-ins to meet the technical requirements.
Where can you find the column name to complete the where clause?- ASecurity alerts in Azure Security Center
- BActivity log in Azure
- CAzure Advisor
- Dthe query windows of the Log Analytics workspace
Show answer
Correct answer: D
WhyThe case study text is missing. Column names for the failed sign-in query, such as ResultType in SigninLogs, are found by browsing the table schema in the query window of the Log Analytics workspace. Defender for Cloud alerts, the Activity log and Azure Advisor do not show table schemas.
- A
- You need to restrict cloud apps running on CLIENT1 to meet the Microsoft Defender for Endpoint requirements.
Which two configurations should you modify? Each correct answer present part of the solution.
NOTE: Each correct selection is worth one point.- Athe Onboarding settings from Device management in Microsoft Defender Security Center
- BCloud App Security anomaly detection policies
- CAdvanced features from Settings in Microsoft Defender Security Center
- Dthe Cloud Discovery settings in Cloud App Security
Show answer
Correct answer: C, D
WhyThe case study text is missing. Blocking unsanctioned cloud apps on Defender for Endpoint devices requires turning on the Microsoft Defender for Cloud Apps integration in Defender for Endpoint Advanced features and enabling enforcement in the Cloud Discovery settings of Defender for Cloud Apps, so unsanctioned apps are blocked through network protection.
- A