

SC-900 sample exam questions
15 exam-style questions for Microsoft SC-900: Security, Compliance, and Identity Fundamentals, with answers and explanations. Take them as a timed practice exam first if you want a score out of 1000.
- In the Microsoft Cloud Adoption Framework for Azure, which two phases are addressed before the Ready phase? Each correct answer presents a complete
solution.
NOTE: Each correct selection is worth one point.- APlan
- BManage
- CAdopt
- DGovern
- EDefine Strategy
Show answer
Correct answer: A, E
WhyThe Cloud Adoption Framework phases run Define Strategy, Plan, Ready, Adopt, with Govern and Manage running alongside them. So Define Strategy and Plan come before Ready, while Adopt follows it and Govern and Manage are ongoing.
- A
- Which three authentication methods can be used by Azure Multi-Factor Authentication (MFA)? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.- Atext message (SMS)
- BMicrosoft Authenticator app
- Cemail verification
- Dphone call
- Esecurity question
Show answer
Correct answer: A, B, D
WhyMicrosoft Entra multifactor authentication (formerly Azure MFA) supports the Microsoft Authenticator app, SMS text messages and voice phone calls, as well as OATH tokens and FIDO2 keys. Email verification and security questions are only used for self-service password reset, not MFA.
- A
- You plan to implement a security strategy and place multiple layers of defense throughout a network infrastructure.
Which security methodology does this represent?- Athreat modeling
- Bidentity as the security perimeter
- Cdefense in depth
- Dthe shared responsibility model
Show answer
Correct answer: C
WhyDefense in depth uses several layers of protection (physical, identity, perimeter, network, compute, application, data), so if one layer is breached the others still protect the asset. Threat modeling finds threats during design, and the shared responsibility model splits duties between Microsoft and the customer.
- A
- Which type of alert can you manage from the Microsoft 365 Defender portal?
- AMicrosoft Defender for Storage
- BMicrosoft Defender for SQL
- CMicrosoft Defender for Endpoint
- DMicrosoft Defender for IoT
Show answer
Correct answer: C
WhyThe Microsoft Defender portal (formerly Microsoft 365 Defender) manages alerts from Defender for Endpoint, Office 365, Identity and Cloud Apps. Defender for Storage, SQL and IoT were traditionally Defender for Cloud and Azure alerts, so Defender for Endpoint is the expected answer.
- A
- What are customers responsible for when evaluating security in a software as a service (SaaS) cloud services model?
- Aoperating systems
- Bnetwork controls
- Capplications
- Daccounts and identities
Show answer
Correct answer: D
WhyIn SaaS, the provider manages the application, operating system, network controls and infrastructure. The customer always keeps responsibility for their information and data, devices, and accounts and identities.
- A
- HOTSPOT
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
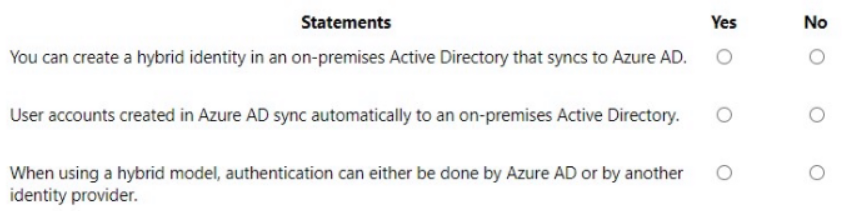
You can create a hybrid identity in an on-premises Active Directory that syncs to Azure AD. Yes / No User accounts created in Azure AD sync automatically to an on-premises Active Directory. Yes / No When using a hybrid model, authentication can either be done by Azure AD or by another identity provider. Yes / No Show answer
- You can create a hybrid identity in an on-premises Active Directory that syncs to Azure AD. Yes
- User accounts created in Azure AD sync automatically to an on-premises Active Directory. No
- When using a hybrid model, authentication can either be done by Azure AD or by another identity provider. Yes
WhyHybrid identities are created in on-premises AD and synced to Microsoft Entra ID (formerly Azure AD) by Entra Connect. Cloud-only accounts are not synced back to AD by default. Authentication can use password hash sync or pass-through authentication in Entra ID, or federation with another provider such as AD FS.
- What are two reasons to deploy multiple virtual networks instead of using just one virtual network? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.- Ato meet governance policies
- Bto connect multiple types of resources
- Cto separate the resources for budgeting
- Dto isolate the resources
Show answer
Correct answer: A, D
WhyOrganizations deploy several virtual networks to isolate resources from each other (segmentation) and to meet governance policies that require separate environments or owners. One VNet can already hold many kinds of resources, and budgeting separation is usually done with subscriptions, resource groups or tags.
- A
- Which score measures an organization’s progress in completing actions that help reduce risks associated to data protection and regulatory standards?
- AAdoption Score
- BMicrosoft Secure Score
- CSecure score in Microsoft Defender for Cloud
- DCompliance score
Show answer
Correct answer: D
WhyCompliance score in Microsoft Purview Compliance Manager tracks completion of improvement actions that reduce data protection and regulatory risk. Microsoft Secure Score and Defender for Cloud secure score measure security posture, and Adoption Score measures how people use Microsoft 365.
- A
- HOTSPOT
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
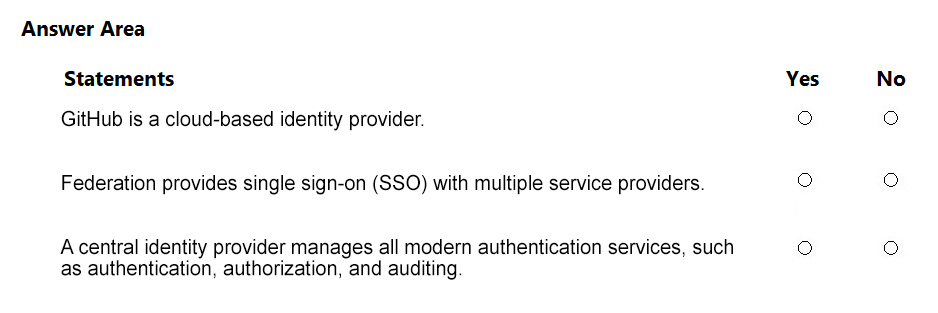
GitHub is a cloud-based identity provider. Yes / No Federation provides single sign-on (SSO) with multiple service providers. Yes / No A central identity provider manages all modern authentication services, such as authentication, authorization, and auditing. Yes / No Show answer
- GitHub is a cloud-based identity provider. Yes
- Federation provides single sign-on (SSO) with multiple service providers. Yes
- A central identity provider manages all modern authentication services, such as authentication, authorization, and auditing. Yes
WhyMicrosoft Learn lists GitHub, alongside Microsoft, Google and Facebook, as a cloud identity provider. Federation creates trust between domains so one sign-in works across several service providers. With modern authentication, a central identity provider handles authentication, authorization and auditing services.
- When you enable Azure AD Multi-Factor Authentication (MFA), how many factors are required for authentication?
- A1
- B2
- C3
- D4
Show answer
Correct answer: B
WhyMultifactor authentication needs at least two different factors, for example something you know (a password) plus something you have (the Authenticator app or a phone) or something you are (biometrics). So Microsoft Entra MFA, formerly Azure AD MFA, requires two factors.
- A
- HOTSPOT
Select the answer that correctly completes the sentence.
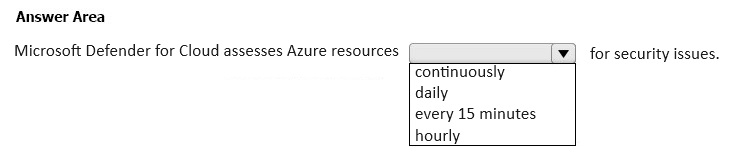
Microsoft Defender for Cloud assesses Azure resources ___ for security issues. continuously / daily / every 15 minutes / hourly Show answer
- Microsoft Defender for Cloud assesses Azure resources ___ for security issues. continuously
WhyMicrosoft Defender for Cloud continuously assesses Azure, hybrid and multicloud resources for security issues and updates its recommendations and secure score. It does not run on a fixed daily, hourly or 15-minute schedule.
- HOTSPOT
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
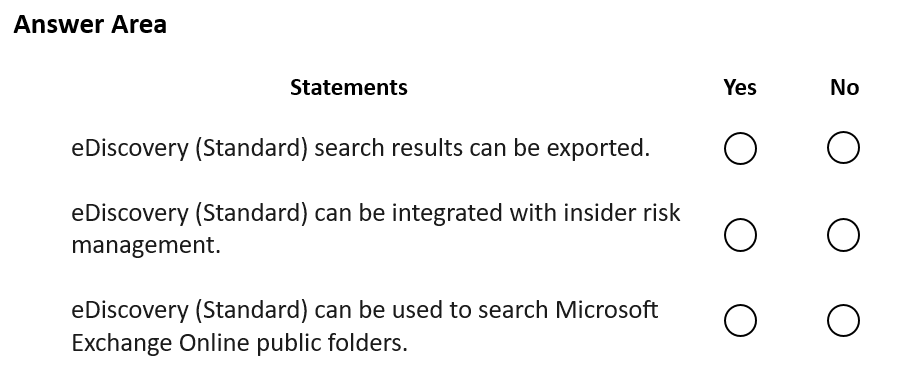
eDiscovery (Standard) search results can be exported. Yes / No eDiscovery (Standard) can be integrated with insider risk management. Yes / No eDiscovery (Standard) can be used to search Microsoft Exchange Online public folders. Yes / No Show answer
- eDiscovery (Standard) search results can be exported. Yes
- eDiscovery (Standard) can be integrated with insider risk management. No
- eDiscovery (Standard) can be used to search Microsoft Exchange Online public folders. Yes
WhyeDiscovery (Standard) lets you create cases, search content locations including Exchange public folders, place holds and export results. Escalating insider risk cases to eDiscovery is a Premium capability. Note: Standard and Premium are now merged into the unified eDiscovery experience in the Purview portal.
- Which two actions can you perform by using Azure Key Vault? Each correct answer presents a complete solution.
NOTE: Each correct selection is worth one point.- AStore secrets.
- BStore Azure Resource Manager (ARM) templates.
- CImplement network security groups (NSGs).
- DImplement Azure DDoS Protection.
- EStore keys.
Show answer
Correct answer: A, E
WhyAzure Key Vault stores secrets (passwords, connection strings), cryptographic keys and certificates. ARM templates belong in a repository or Template Specs, and NSGs and DDoS Protection are network security services configured separately.
- A
- HOTSPOT
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Microsoft Entra Access Review evaluates user and group permissions for Azure resources. Yes / No A user can be removed from a group automatically after a Microsoft Entra Access Review evaluation. Yes / No The Microsoft Entra Access Review feature is available in all Microsoft Entra ID service plans. Yes / No Show answer
- Microsoft Entra Access Review evaluates user and group permissions for Azure resources. Yes
- A user can be removed from a group automatically after a Microsoft Entra Access Review evaluation. Yes
- The Microsoft Entra Access Review feature is available in all Microsoft Entra ID service plans. No
WhyAccess reviews can cover group membership, application access and Azure resource roles (via PIM), and the auto-apply setting removes denied users automatically. The feature requires Microsoft Entra ID P2 or Microsoft Entra ID Governance licences, not the Free plan.
- To which three locations can a data loss prevention (DLP) policy be applied? Each correct answer presents a complete solution.
NOTE: Each correct answer is worth one point.- AMicrosoft Exchange Online email
- BMicrosoft OneDrive accounts
- CMicrosoft Exchange Online public folders
- DMicrosoft Teams chat and channel messages
- EMicrosoft Viva Engage
Show answer
Correct answer: A, B, D
WhyMicrosoft Purview DLP policies can apply to Exchange Online email, SharePoint sites, OneDrive accounts, Teams chat and channel messages, devices and more. Exchange public folders are not a supported DLP location, and Viva Engage is not one of the expected answers.
- A